
إعلان
Lovax.net
استخدام lovable unlimited بدون حدود
أعرف المزيد
كاسبرسكي | رصد فريق البحث والتحليل العالمي (GReAT) في شركة كاسبرسكي حملة سيبرانية متطورة ومتعددة المراحل تستهدف المستخدمين الأفراد والمؤسسات، عبر إخفاء برمجيات خبيثة
استخدام lovable unlimited بدون حدود
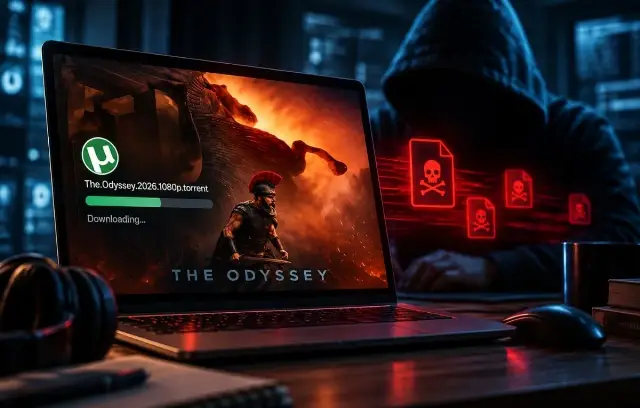
أعرف المزيدرصد فريق البحث والتحليل العالمي (GReAT) في شركة كاسبرسكي حملة سيبرانية متطورة ومتعددة المراحل تستهدف المستخدمين الأفراد والمؤسسات، عبر إخفاء برمجيات خبيثة غير معروفة سابقًا داخل ملفات تورنت لأفلام شهيرة، منها فيلم “The Odyssey” الجديد.
وحدد الباحثون مئات الضحايا في دول عدة، منها روسيا وتركيا واليابان وكينيا وأوغندا وكولومبيا، بالإضافة إلى دول أوروبية مثل إسبانيا وهولندا وبلجيكا وألمانيا. وتشمل قائمة الضحايا مؤسسات تعمل في قطاعات الأعمال والحكومة وتكنولوجيا المعلومات والاستشارات وتجارة التجزئة والنقل والزراعة.
وبحسب كاسبرسكي، فقد بدأ نشاط الحملة في منتصف أغسطس 2026، وما زال مستمرًا حتى الآن. واستغل المهاجمون اختراق أحد مواقع الأرشيف العامة المستخدمة لتخزين ملفات التورنت، لنشر البرمجيات الخبيثة والوصول إلى المستخدمين.
صمم المهاجمون الحملة على هيئة إطار عمل متعدد المراحل، تتكامل مكوناته لتنفيذ عمليات الاختراق وتوسيع نطاق السيطرة على الأجهزة المصابة.
وتبدأ العملية باستخدام أداة تحميل خبيثة قادرة على اكتشاف بيئات الاختبار المعزولة التي تستخدمها برامج مكافحة الفيروسات لفحص الملفات المشبوهة. ويساعد ذلك البرمجية على تحديد ما إذا كانت تخضع للتحليل الأمني، واتخاذ إجراءات للتخفي وتفادي الاكتشاف أو عرقلة التحقيقات اللاحقة.
وبعد تفعيل البرمجية في جهاز الضحية، يمكنها نشر وحدات إضافية تتيح لها الحفاظ على وجودها داخل النظام حتى بعد إعادة تشغيل الجهاز أو إنهاء العملية الخبيثة.
وتتضمن قدراتها تجاوز خاصية التحكم في حساب المستخدم (UAC) في نظام ويندوز، بهدف الحصول على صلاحيات المسؤول دون إظهار رسالة التحذير المعتادة، وهو ما يتيح للمهاجمين الوصول إلى الأجهزة المصابة من بُعد.
تعتمد الحملة على سلسلة الكتل Solana للحصول على عنوان خادم القيادة والتحكم (C2) الذي يستخدمه المهاجمون لإدارة البرمجيات الخبيثة والتواصل مع الأجهزة المصابة.
ويساعد هذا الأسلوب المهاجمين على تعزيز مرونة بنيتهم التحتية، ويزيد صعوبة تعطيل الحملة عبر حظر الخوادم أو تفكيكها.
كاسبرسكي: ملفات الترفيه قد تتحول إلى وسيلة للاختراق
وقال قسطنطين إيساكوف، خبير الأمن السيبراني في فريق البحث والتحليل العالمي لدى كاسبرسكي:
“تجمع هذه الحملة الخبيثة بين وسيلة إغراء شائعة وبنية تقنية متطورة. فمن خلال تمويه البرمجية الخبيثة على هيئة ملفات تورنت لأفلام شهيرة، يزيد المهاجمون احتمال تحميلها من المستخدمين غير الحذرين.
وبمجرد تشغيلها، تستطيع هذه البرمجية متعددة المراحل تفادي الاكتشاف، وضمان استمرارية وجودها في النظام، ومنح المهاجمين وصولًا من بُعد إلى الأجهزة المصابة.
لذلك، ينبغي للمستخدمين توخي الحذر عند تحميل الملفات من مصادر غير رسمية؛ إذ قد يتحول حتى المحتوى الترفيهي الذي يبدو غير ضار إلى وسيلة لاختراق الأنظمة”.
دعت كاسبرسكي المستخدمين إلى اتباع مجموعة من الإجراءات للحد من مخاطر الإصابة بالبرمجيات الخبيثة، تشمل:
كما أوصت الشركة المؤسسات باتخاذ تدابير لتعزيز أمن أجهزتها وشبكاتها، من أبرزها:
وأكدت كاسبرسكي أن حلولها الأمنية اكتشفت البرمجيات الخبيثة المستخدمة في الحملة، مشيرةً إلى إتاحة التحليل التقني الكامل
Kaspersky's Global Research and Analysis Team (GReAT) has detected a sophisticated, multi-stage cyber campaign targeting individual and institutional users, by hiding previously unknown malware inside torrents of popular movies, including the new movie “The Odyssey.”
The researchers identified hundreds of victims in several countries, including Russia, Turkey, Japan, Kenya, Uganda and Colombia, in addition to European countries such as Spain, the Netherlands, Belgium and Germany. The list of victims includes institutions operating in the business, government, IT, consultancy, retail, transport and agriculture sectors.
According to Kaspersky, the campaign activity started in mid-August 2026, and it is still ongoing so far. The attackers exploited the hacking of one of the public archive sites used to store torrents to spread malware and reach users.
The attackers designed the campaign in the form of a multi-stage framework, whose components are integrated to carry out hacking operations and expand the scope of control over infected devices.
The process begins with a malicious downloader capable of detecting the isolated testing environments that antivirus programs use to scan suspicious files. This helps the software to determine whether it is subject to security analysis, take actions to hide and avoid detection or hinder subsequent investigations.
After the software is activated in the victim's device, it can deploy additional modules that allow it to maintain its presence within the system even after the device is restarted or the malicious process is terminated.
Its capabilities include bypassing the user account control (UAC) feature in Windows, in order to obtain administrator privileges without showing the usual warning message, which allows attackers to access infected devices remotely.
The campaign relies on the Solana blockchain to obtain the C2 server address that attackers use to manage malware and communicate with infected devices.
This approach helps attackers enhance the resilience of their infrastructure, and makes it more difficult to disrupt the campaign by blocking or dismantling servers.
Kaspersky: Entertainment files may turn into a means of hacking
Konstantin Isakov, a cybersecurity expert in Kaspersky's Global Research and Analysis Team, said:
“This malicious campaign combines a common lure with a sophisticated technology architecture. By disguising malware as torrents of popular movies, attackers increase the likelihood that they will be downloaded from unwary users.
Once activated, this multi-stage software can evade detection, ensure its continued presence in the system, and grant attackers remote access to infected devices.
Therefore, users should exercise caution when downloading files from unofficial sources; even seemingly innocuous entertainment content may turn into a means of hacking systems. ”
Kaspersky called on users to follow a set of measures to reduce the risk of malware infection, including:
The company also recommended institutions to take measures to enhance the security of their devices and networks, the most prominent of which are:
Kaspersky confirmed that its security solutions discovered the malware used in the campaign, noting that full technical analysis
Software Engineer & AI Builder
مطور برمجيات متكامل ومصمم جرافيك مع أكثر من 4 سنوات خبرة في بناء تطبيقات الويب الحديثة باستخدام PHP و JavaScript و HTML و CSS. خلفية قوية في تصميم UI/UX واستخدام متقدم لأدوات الذكاء الاصطناعي لتعزيز كفاءة التطوير والأتمتة واتخاذ القرارات. حاصل على ماجستير تنفي...
التعليقات (0)
كن أول من يعلّق على هذا المقال.